Why Dark Web Monitoring Matters
Dark web monitoring helps protect your business by identifying exposed data before it can be exploited. Below are the key benefits and value propositions of incorporating dark web monitoring into your cybersecurity strategy.
Early Detection
Identify compromised credentials and sensitive information before hackers can exploit them.
Reduce Manual Effort
We handle the monitoring, allowing you to focus on daily operations while staying protected.
Protect Your Reputation
Prevent public breaches and keep your organization out of damaging headlines.
Enhanced Security
Receive actionable insights to strengthen your security protocols, change passwords, and update defenses as soon as threats are detected.
How CIRRUS Protects You
When it Comes to Dark Web Monitoring
24/7/365 Monitoring
Continuous scanning of the dark web for any data leaks associated with your domain, including email addresses, passwords, and financial information.
Real-Time Alerts
Be instantly notified when new breaches are detected, allowing for immediate action.
Comprehensive Reports
Receive detailed reports outlining all compromised data, with recommendations to mitigate risks.
Supply Chain Security
Monitor third-party vendors and partners to ensure security beyond your organization.
Trending Resources
By David Dlug Why Unpatched Legacy Software Is Still a Top Attack Vector Meta Description: Learn why unpatched legacy software […]
By Jason Zanetti For good reason, multi-factor authentication (MFA) has become a foundational cybersecurity control. It adds another layer of […]
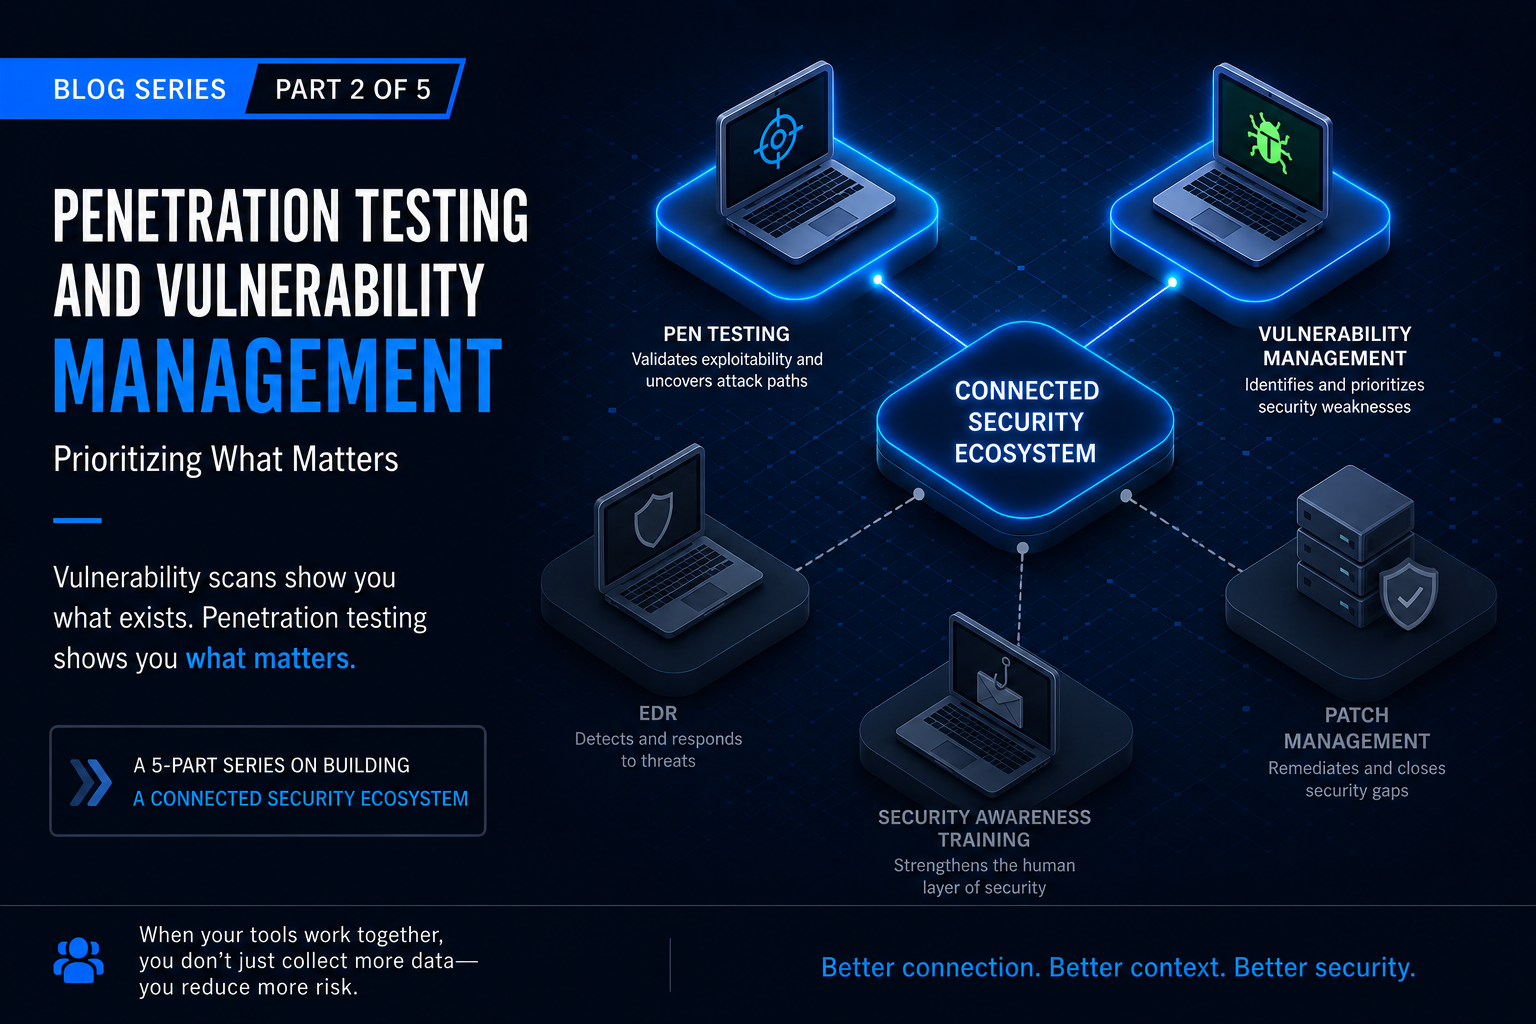
By Trevor Talkowski In the previous post in our Breaking Down Security Silos series, we explored how penetration testing and […]
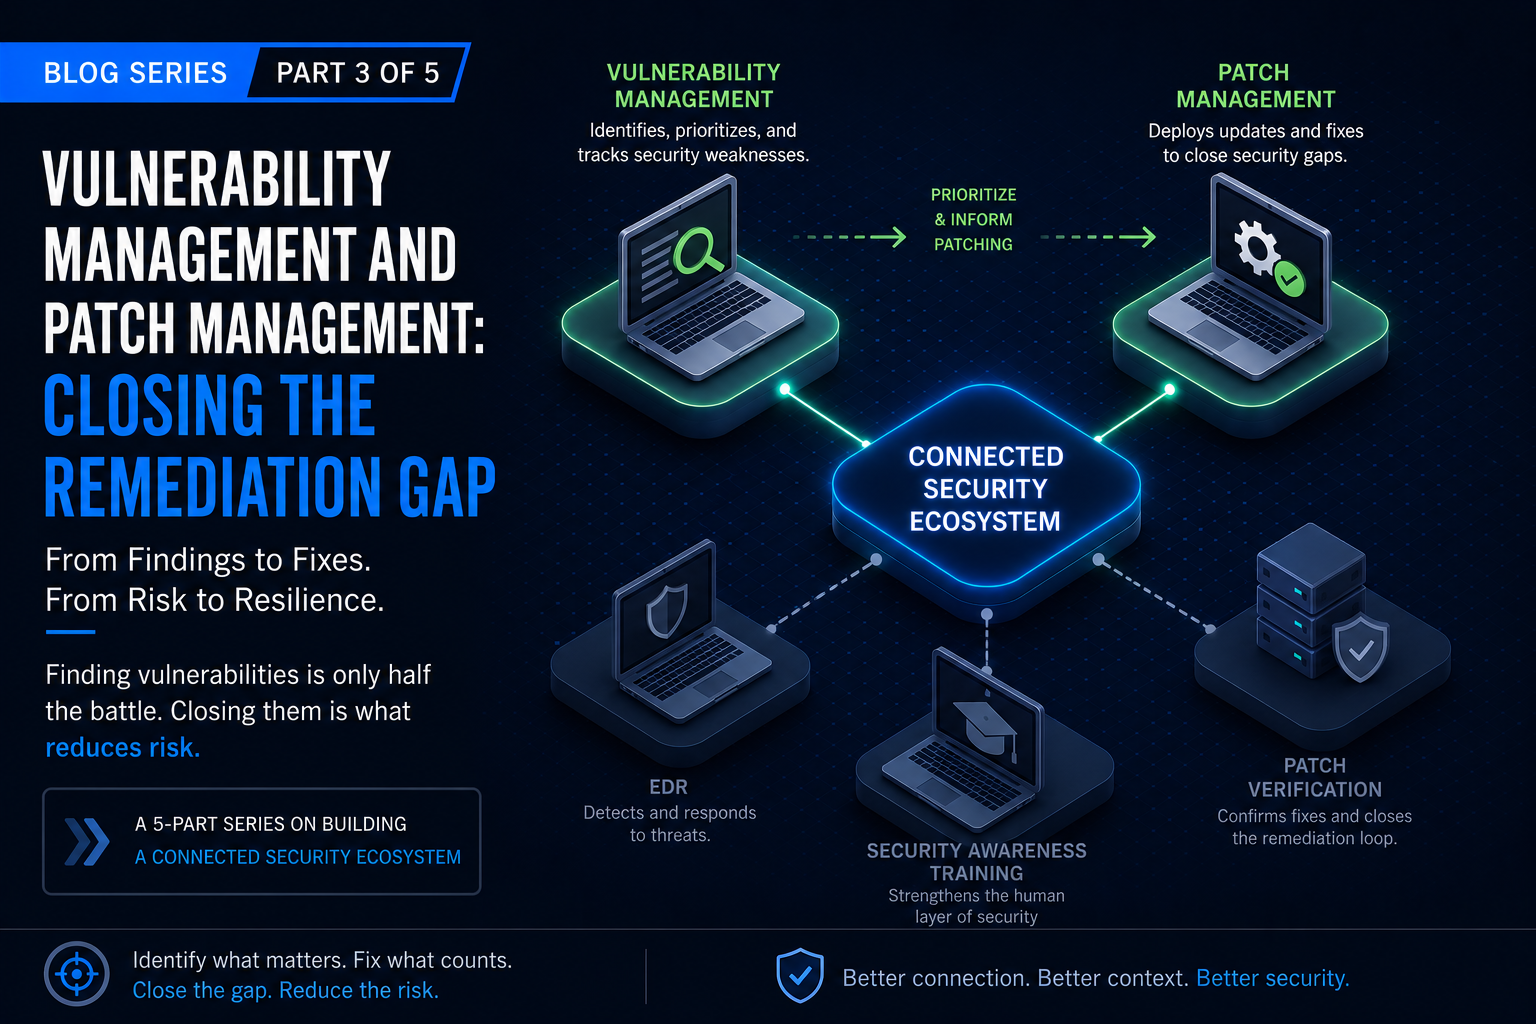
By Will Colleran You Can’t Protect What You Don’t Understand As organizations mature their cybersecurity programs, one conversation comes up repeatedly. Leadership […]
By Diamante Cherry In the first post of this series, we discussed why security tools are most effective when they […]
From the Field: Sales Insights for SMB IT Leaders Insights from the cybersecurity conversations we’re having every day with SMB IT leaders. […]
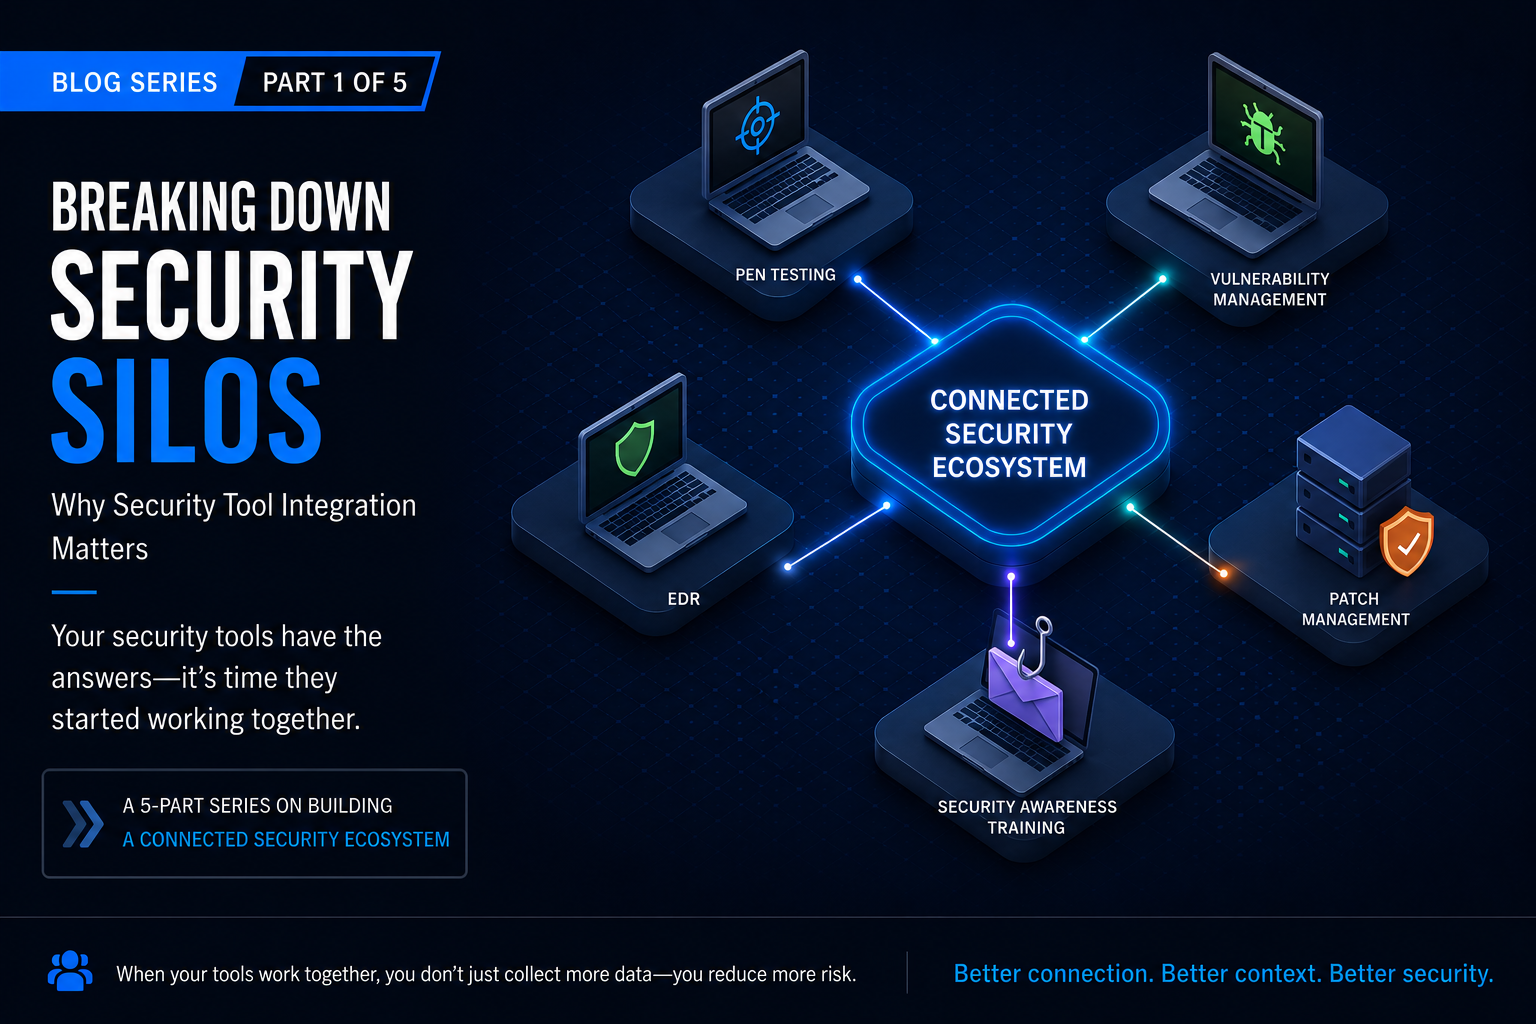
By Anthony Siravo From Building a Security Program to Connecting It In our previous series, we explored the foundational components of a […]
By Shaun Babula The Problem with “One-and-Done” Penetration Testing For many organizations, penetration testing is still treated as a compliance […]