Why Patch Management Matters
Patch management protects your systems by addressing vulnerabilities and keeping software up to date. Below are the key benefits of implementing effective patch management practices.
Cross OS Coverage
Support for Windows, Linux, macOS, and a wide range of third-party applications.
Automated Patch Deployment
Automatically identify and deploy security patches for operating systems and third-party software.
Flexible Scheduling
Customize patch schedules based on your organization’s operational needs.
Continuous Protection
Ensure your operating systems and applications are always up-to-date with the latest security patches.
Rapid Response
Quickly deploy critical patches to safeguard your systems from potential cyber threats and vulnerabilities.
Seamless Compliance
Stay compliant with industry regulations by maintaining secure and patched systems.
How CIRRUS Protects You
When it Comes to Patch Management


Automated Patch Deployment
We apply the necessary patches for both OS and third-party applications, ensuring your systems remain secure at all times.
Collaboration with your Team
Whether you want to manage patches manually or work with us, we offer flexible options tailored to your organization’s needs.
Comprehensive Endpoint Coverage
Our solution covers all your endpoints, consolidating patching across Windows, macOS, and Linux, ensuring no system is left vulnerable.
Trending Resources
By David Dlug Why Unpatched Legacy Software Is Still a Top Attack Vector Meta Description: Learn why unpatched legacy software […]
By Jason Zanetti For good reason, multi-factor authentication (MFA) has become a foundational cybersecurity control. It adds another layer of […]
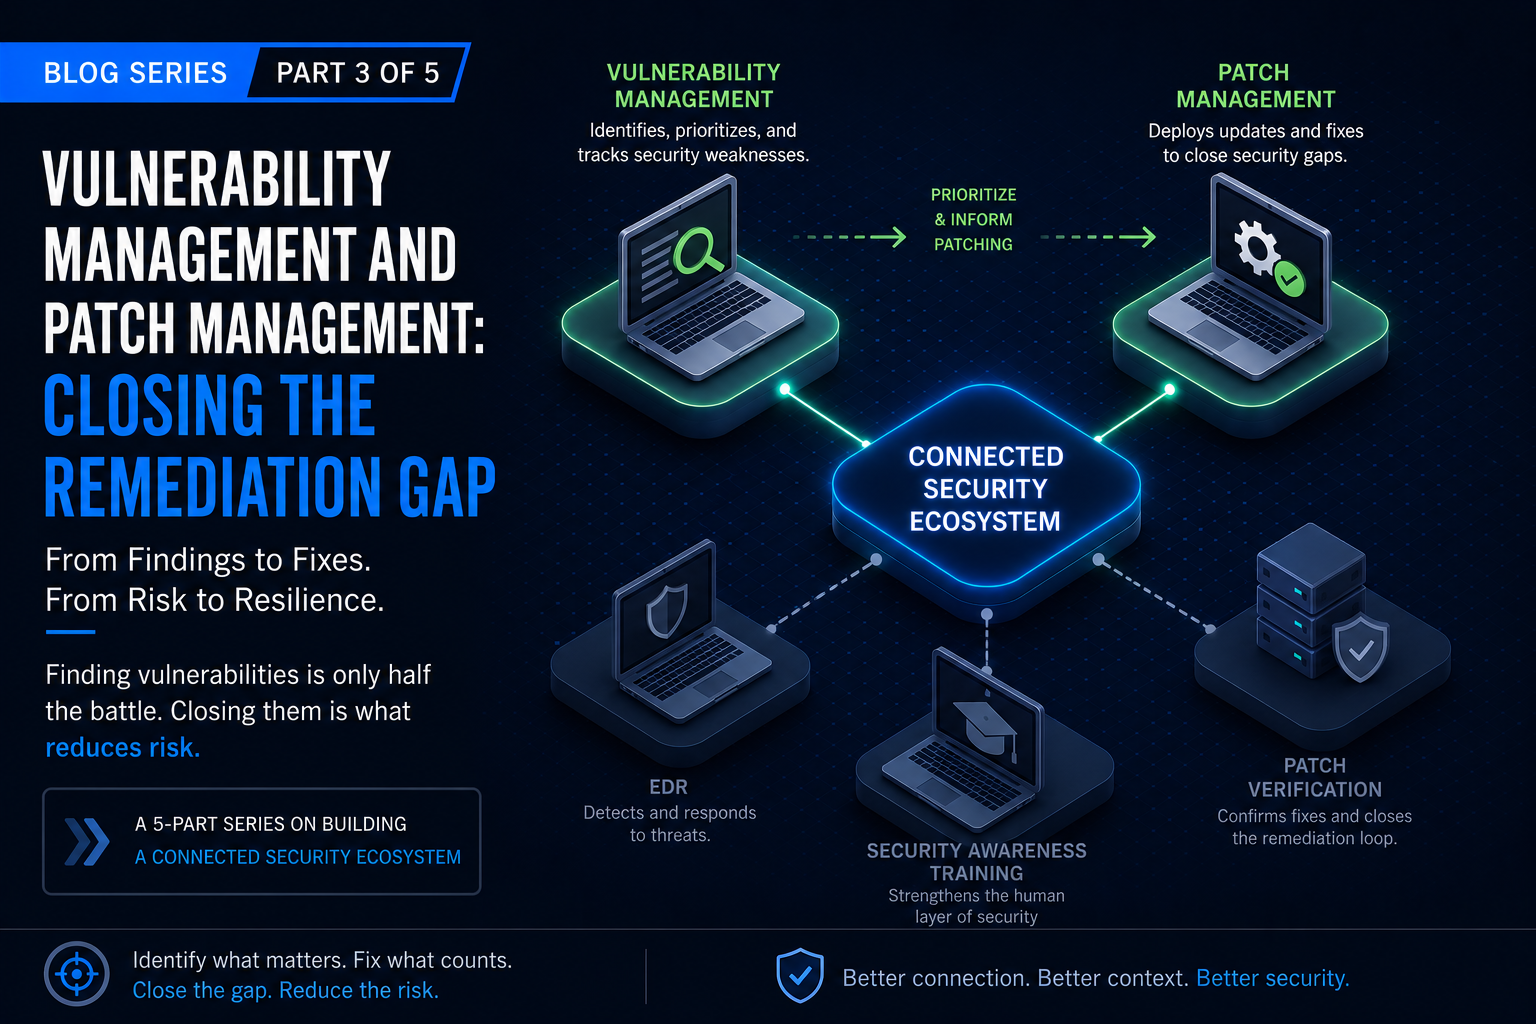
By Trevor Talkowski In the previous post in our Breaking Down Security Silos series, we explored how penetration testing and […]
By Will Colleran You Can’t Protect What You Don’t Understand As organizations mature their cybersecurity programs, one conversation comes up repeatedly. Leadership […]
By Diamante Cherry In the first post of this series, we discussed why security tools are most effective when they […]
From the Field: Sales Insights for SMB IT Leaders Insights from the cybersecurity conversations we’re having every day with SMB IT leaders. […]
By Anthony Siravo From Building a Security Program to Connecting It In our previous series, we explored the foundational components of a […]
By Shaun Babula The Problem with “One-and-Done” Penetration Testing For many organizations, penetration testing is still treated as a compliance […]