Skip to content
  • Services
    • CIRRUS Cybersecurity Stack

      Learn More >>

      Services

      CIRRUS Cybersecurity Solutions
      global-security
      Cybersecurity Overview
      verification
      Network Penetration Testing
      087-management
      Risk Assessment
      monitoring
      Dark Web Monitoring
      CIRRUS Cybersecurity Solutions
      cyber-security
      Phishing Campaigns
      error
      Vulnerability Management
      system-integration
      Patch Management
      cloud-computing
      Data Discovery
      Additional Cybersecurity Solutions
      security-shield
      EDR & XDR
      Business Connectivity Solutions
      process
      Bandwidth, UCaaS, CCaaS
  • Resources
    • Stratus ip Blog

      Stay up-to-date on the latest in cybersecurity, connectivity, and unified communications for small and medium-sized businesses, with the Stratus ip Blog.

      Sign Up Sign Up

      Resources

      • Blog
      • Case Studies
      • Guides
      • Webinars
      • Testimonials
  • Company
    • Company

      • About Us
      • Leadership
      • Culture
      • Giving Back
      • Careers
      • Contact Us
Speak with an Expert Speak with an Expert
  • Services
    • Cybersecurity Overview
    • Network Penetration Testing
    • Risk Assessment
    • Dark Web Monitoring
    • Phishing Campaigns
    • Vulnerability Management
    • Patch Management
    • Data Discovery
    • Bandwidth, UCaaS, CCaaS
    • Advanced EDR & MDR Protection
  • Resources
    • Blog Sign Up
    • Blog
    • Case Studies
    • Webinars
    • Testimonials
  • Company
    • About Us
    • Leadership
    • Culture
    • Giving Back
    • Careers
    • Contact Us
  • Speak with an Expert

Why Unpatched Legacy Software Is Still a Top Attack Vector

Why Unpatched Legacy Software Is Still a Top Attack Vector
  • Cybersecurity
  • Real IT Conversations
  • September 15, 2026

Why Unpatched Legacy Software Is Still a Top Attack Vector

By David Dlug  Why Unpatched Legacy Software Is Still a Top Attack Vector  Meta Description: Learn why unpatched legacy software […]

Read More
The Hidden Risk of Cloud Data Sprawl, Even in MFA-Protected Environments
  • Cybersecurity
  • Real IT Conversations
  • September 2, 2026

The Hidden Risk of Cloud Data Sprawl, Even in MFA-Protected Environments

By Jason Zanetti For good reason, multi-factor authentication (MFA) has become a foundational cybersecurity control. It adds another layer of […]

Read More
Vulnerability Management and Patch Management: Closing the Remediation Gap | Part 3
  • Cybersecurity
  • Security Silos
  • August 20, 2026

Vulnerability Management and Patch Management: Closing the Remediation Gap | Part 3

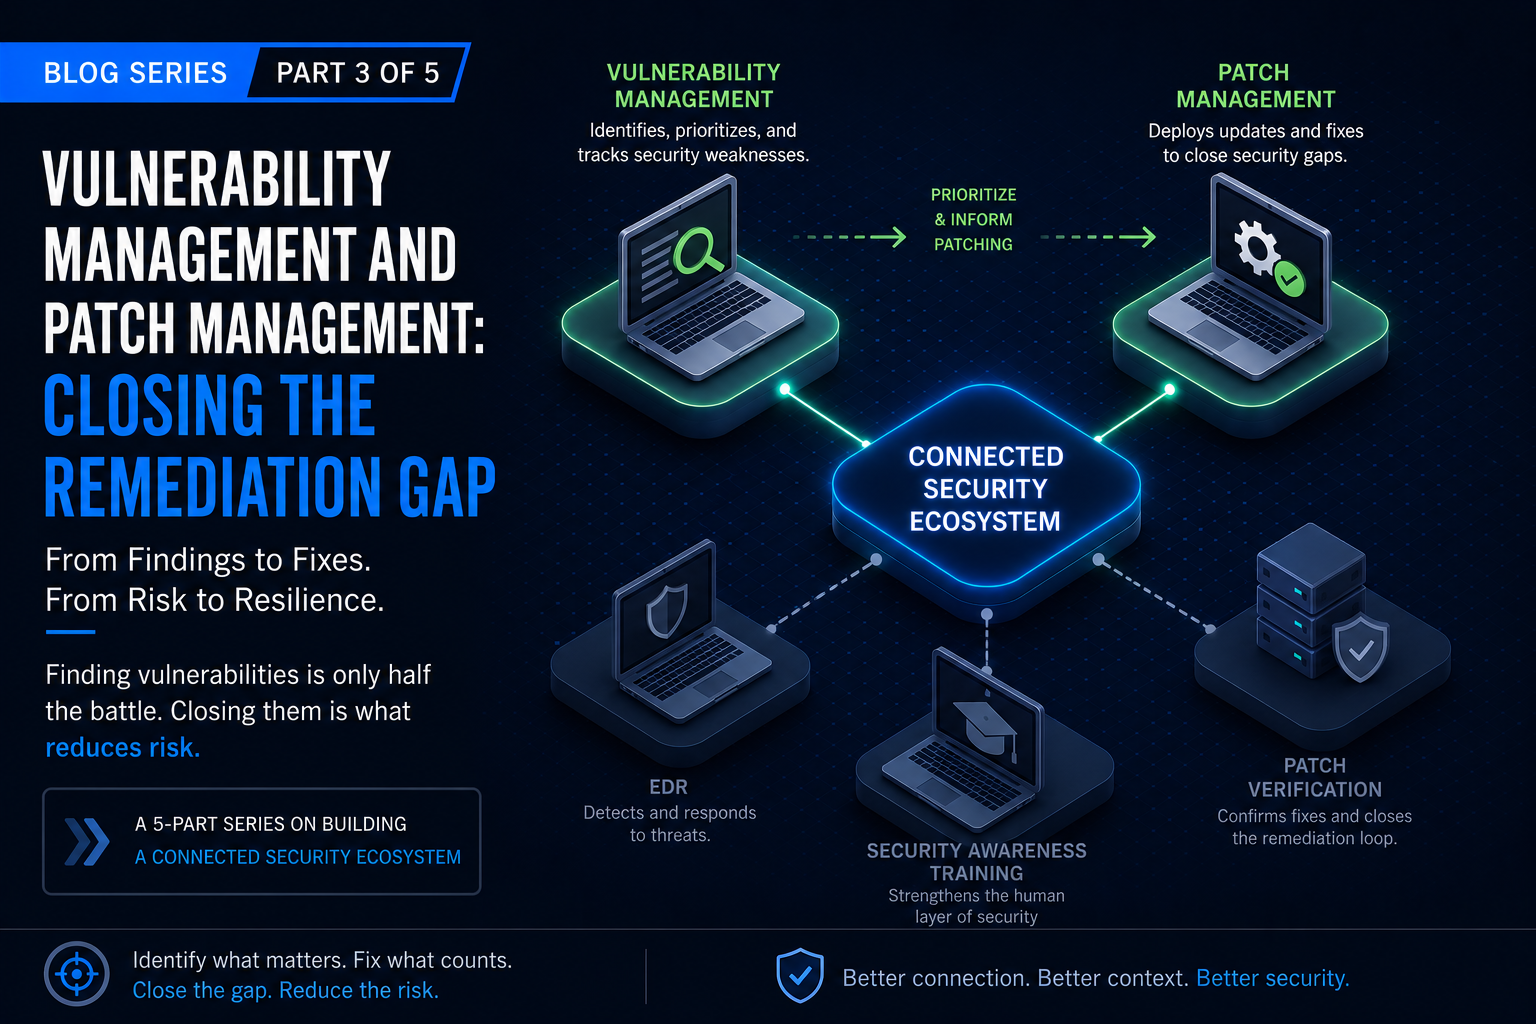
By Trevor Talkowski  In the previous post in our Breaking Down Security Silos series, we explored how penetration testing and […]

Read More
Before You Restrict Access, Know Your Data: Why Visibility Comes First
  • Cybersecurity
  • August 6, 2026

Before You Restrict Access, Know Your Data: Why Visibility Comes First

By Will Colleran You Can’t Protect What You Don’t Understand As organizations mature their cybersecurity programs, one conversation comes up repeatedly. Leadership […]

Read More
Penetration Testing vs. Vulnerability Management: Why Both Matter | Part 2 of Breaking Down Security Silos
  • Cybersecurity
  • Security Silos
  • July 15, 2026

Penetration Testing vs. Vulnerability Management: Why Both Matter | Part 2 of Breaking Down Security Silos

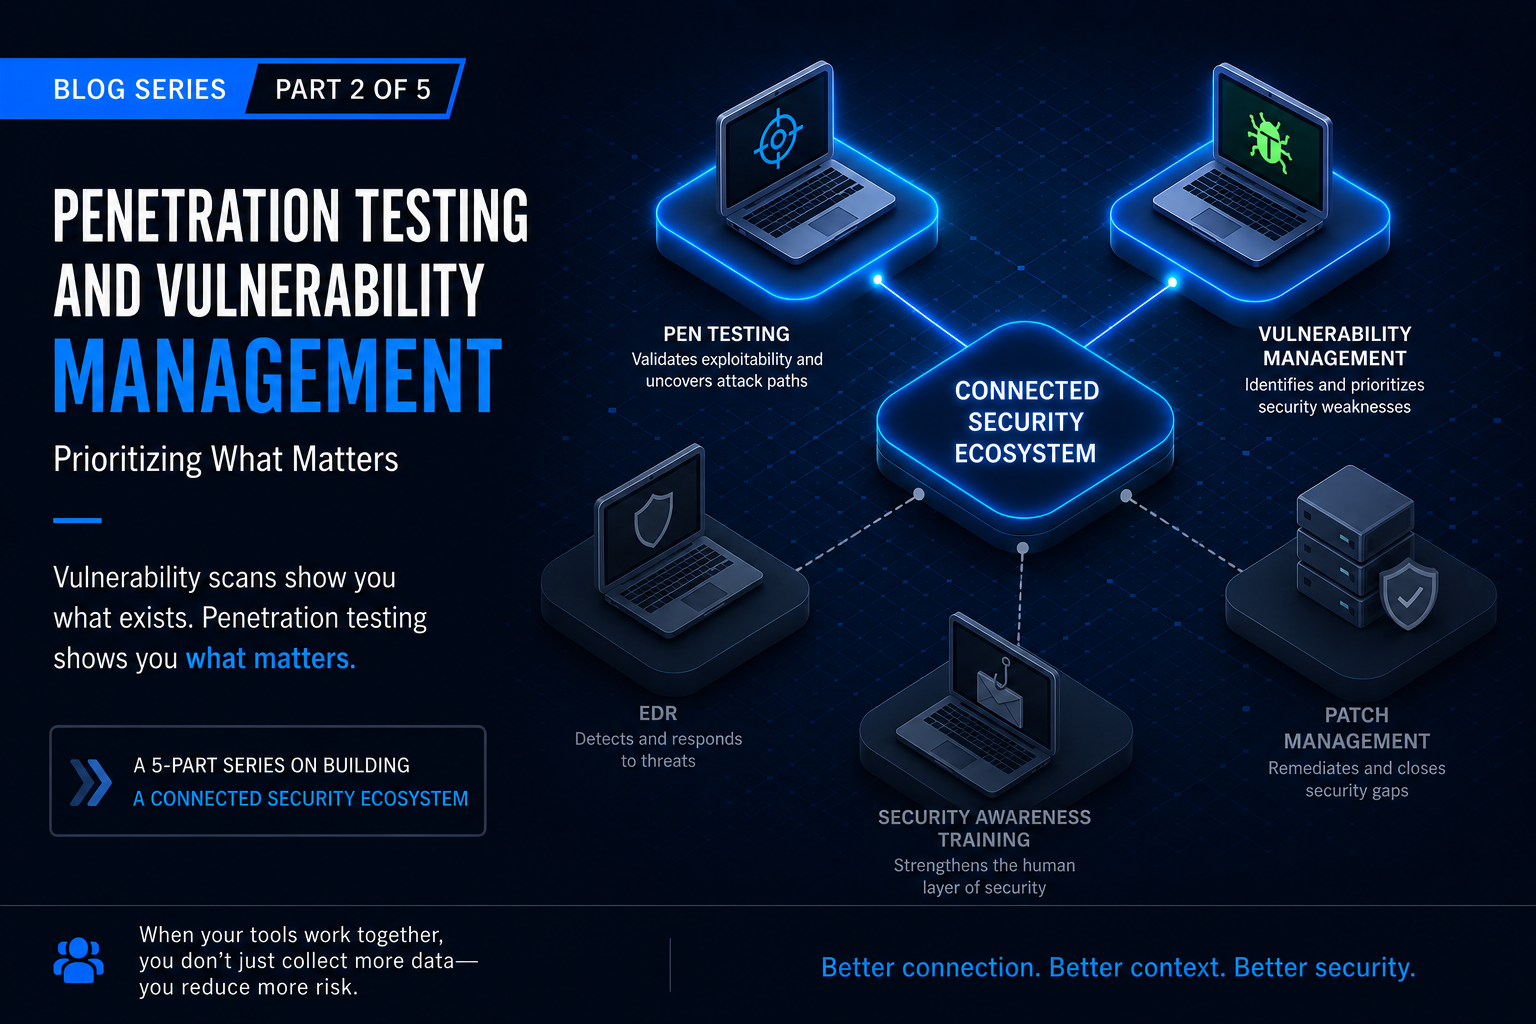
By Diamante Cherry In the first post of this series, we discussed why security tools are most effective when they […]

Read More
Why Secure Defaults Aren’t Enough: The Importance of Assessing Microsoft 365 and Google Workspace Configurations
  • Cybersecurity
  • Real IT Conversations
  • July 8, 2026

Why Secure Defaults Aren’t Enough: The Importance of Assessing Microsoft 365 and Google Workspace Configurations

From the Field: Sales Insights for SMB IT Leaders  Insights from the cybersecurity conversations we’re having every day with SMB IT leaders.  […]

Read More
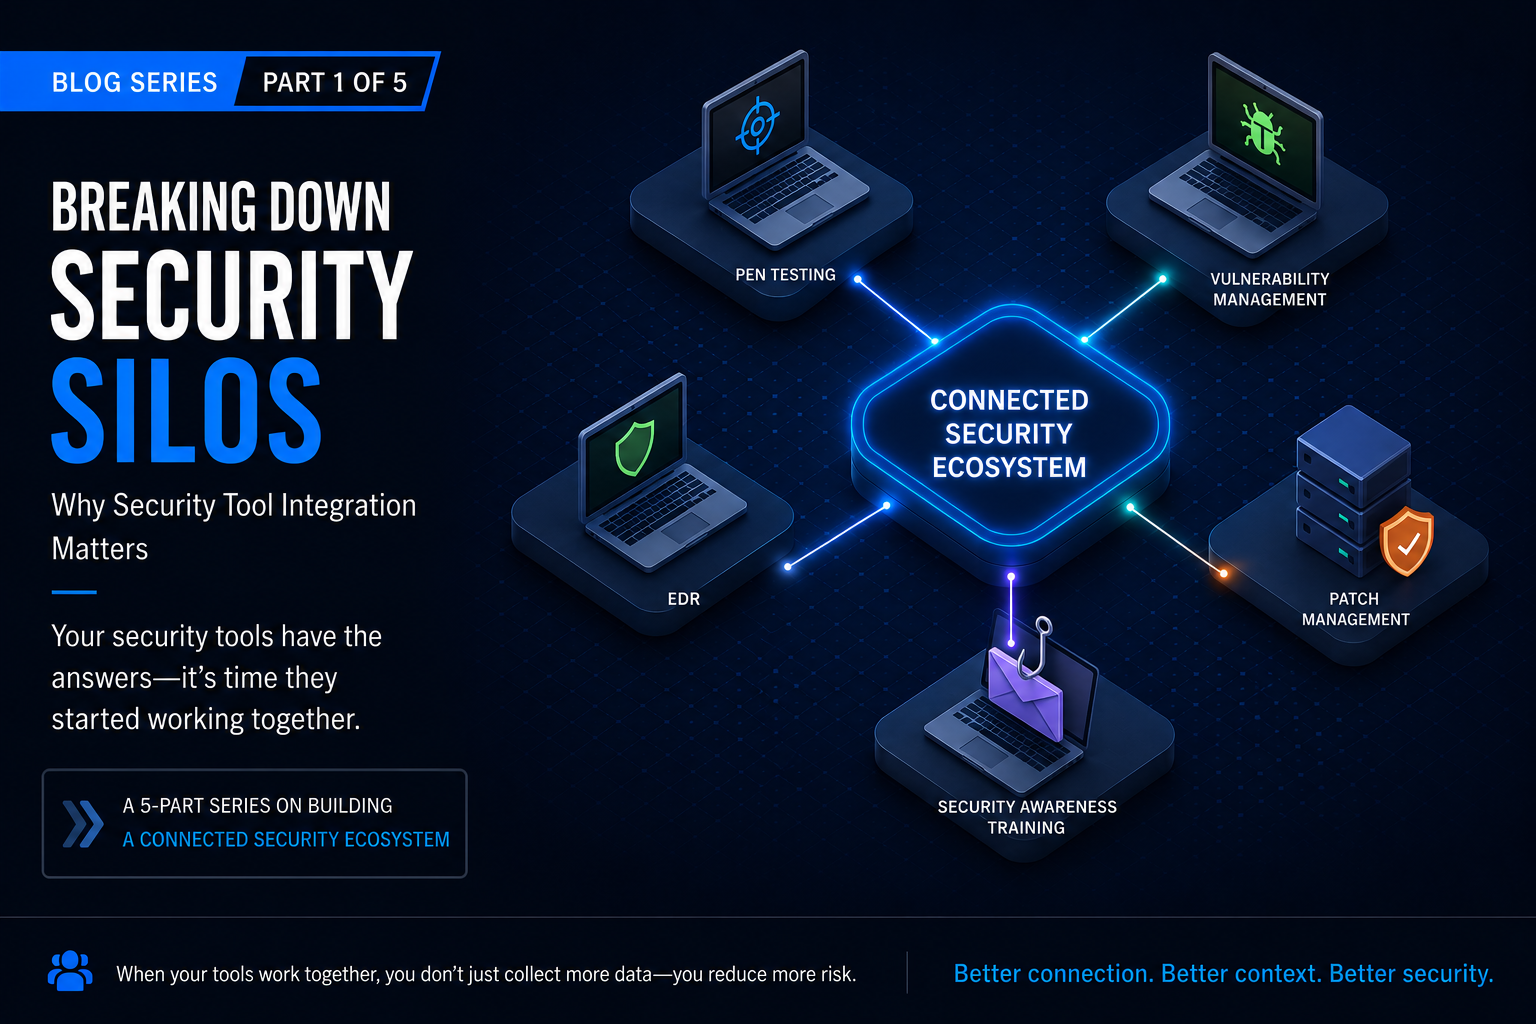
Security Tool Integration for IT Leaders: Breaking Down Security Silos | Part 1
  • Cybersecurity
  • Security Silos
  • June 24, 2026

Security Tool Integration for IT Leaders: Breaking Down Security Silos | Part 1

By Anthony Siravo  From Building a Security Program to Connecting It  In our previous series, we explored the foundational components of a […]

Read More
Why Annual “Check-the-Box” Penetration Testing Isn’t Enough for SMB Security
  • Cybersecurity
  • Penetration Testing
  • June 12, 2026

Why Annual “Check-the-Box” Penetration Testing Isn’t Enough for SMB Security

By Shaun Babula  The Problem with “One-and-Done” Penetration Testing  For many organizations, penetration testing is still treated as a compliance […]

Read More
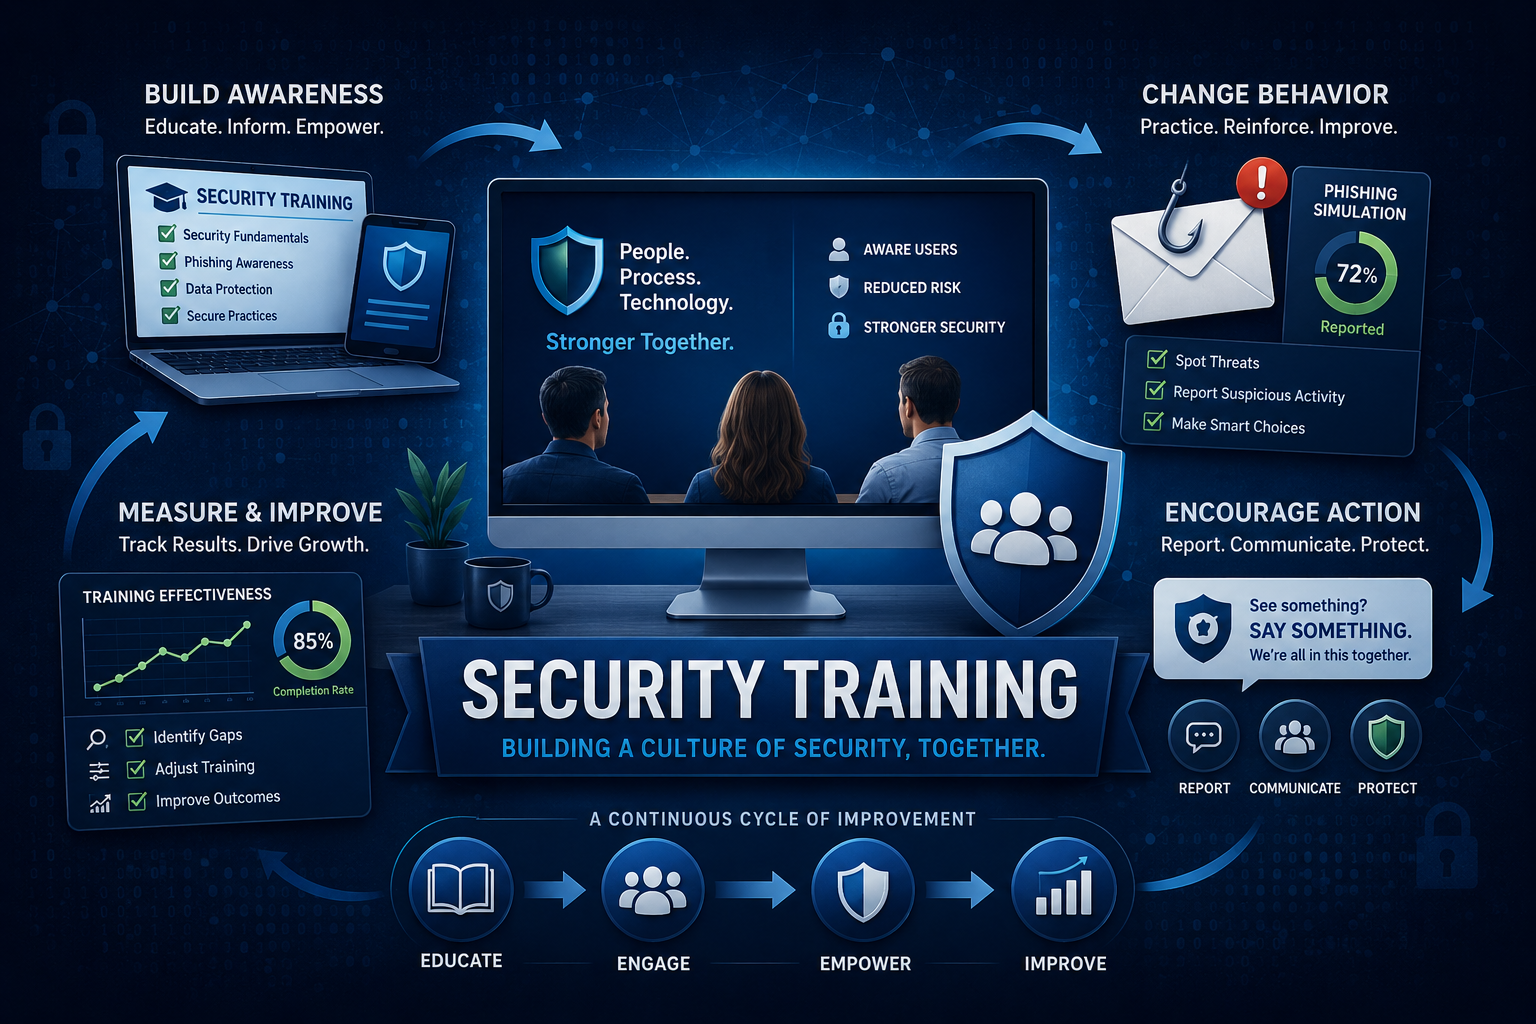
Security Awareness Training: Strengthening the Human Layer of the Security Program
  • Cybersecurity
  • Security Program
  • May 22, 2026

Security Awareness Training: Strengthening the Human Layer of the Security Program

By Chris Stavalone Throughout this series, we have focused on the technical and operational components of a mature security program: identifying risk, […]

Read More
Penetration Testing: More Than Just Finding Outdated Systems
  • Cybersecurity
  • May 6, 2026

Penetration Testing: More Than Just Finding Outdated Systems

By Jason Zanetti The Misconception: “We Already Know What a Pen Test Will Find”  One of the most common objections […]
Read More
  • 1
  • 2
  • 3
  • …
  • 5

Asides

Recent Post

    • September 15, 2026
    Why Unpatched Legacy Software Is Still a Top Attack Vector
    • September 2, 2026
    The Hidden Risk of Cloud Data Sprawl, Even in MFA-Protected Environments
    • August 20, 2026
    Vulnerability Management and Patch Management: Closing the Remediation Gap | Part 3

Categories

  • Bandwith Solution
  • Cybersecurity
  • Hosted Communications
  • Network Services
  • Partnership
  • Penetration Testing
  • Phishing
  • Real IT Conversations
  • Security Program
  • Security Silos
  • Security Silos
  • UCaaS
  • White Papers

See Our Cutting-Edge Solutions In Action

Speak with our experts and see how you can transform your business by improving cybersecurity, connectivity, and communication.

Speak with an ExpertSpeak with an Expert
Stratus ip’s goal has stayed constant since our founding in 2010; to help simplify our customer’s business technology. In a fast-paced world where technology is constantly advancing, Stratus ip leverages our team of experts to help build the right solution for your cybersecurity, voice, and data needs.

Menu

  • About Us
  • Leadership
  • Culture
  • Giving Back
  • Careers
  • Blog
  • Case Studies
  • Testimonials
  • Contact Us

Our Services

  • Cybersecurity Overview
  • Network Penetration Testing
  • Risk Assessment
  • Dark Web Monitoring
  • Phishing Campaigns
  • Vulnerability Management
  • Patch Management
  • Data Discovery
  • Bandwidth, UCaaS, CCaaS

Contact Us

  • 312 West Route 38, Suite 200, Moorestown, NJ 08057
  • info@stratusip.net
  • (888) 396-1236

© 2026 Stratus ip. All Rights Reserved | Privacy Policy

Stratus ipLogo Header Menu
  • Services
    • Cybersecurity Overview
    • Network Penetration Testing
    • Risk Assessment
    • Dark Web Monitoring
    • Phishing Campaigns
    • Vulnerability Management
    • Patch Management
    • Data Discovery
    • Bandwidth, UCaaS, CCaaS
    • Advanced EDR & MDR Protection
  • Resources
    • Blog Sign Up
    • Blog
    • Case Studies
    • Webinars
    • Testimonials
  • Company
    • About Us
    • Leadership
    • Culture
    • Giving Back
    • Careers
    • Contact Us
  • Speak with an Expert